- Product Center
Advanced Certificate Manager
Manage and renew SSL / TLS certificates for your enterprise with Cloudflare Advanced Certificate Manager.
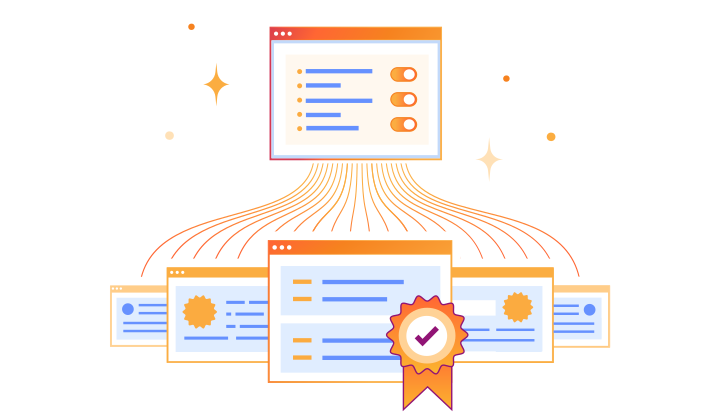
Secure your application with TLS while reducing your team’s workload
Cloudflare Advanced Certificate Manager automatically manages your certificates issuance, management, and renewal with automatic encryption for all new domains you create, customizable for your organizational and regulatory needs. Makes your websites easier to manage, faster, and more secure, from main sites to subdomains.
TLS certificate lifecycle management for websites can be an arduous, manual process, but Cloudflare automatically issues and renews TLS certificates for you.
Customize the hostnames on the certificate, adjust the certificate validity period, select your own certificate authority (CA) and cipher suites, or bring your own certificates.
Cloudflare provides free TLS certificates from our global data centers, ensuring fast loading times for users. We also support the latest, most advanced TLS versions for optimal performance.
Stay on top of data regulations by enabling the most secure cipher suites and TLS 1.3.
HOW IT WORKS
Cloudflare hosts certificates on our global network, enabling faster connections to website visitors no matter where they are.
Cloudflare also makes it easy to adapt TLS certificates for your use case. Add all hostnames to one certificate, encrypt multiple levels of subdomains, choose your own certificate authority (CA), control cipher suites used for TLS, or automatically encrypt all new domains you create.
"Advanced Certificate Manager has simplified the way we manage certificates across our many domains, while still allowing us to meet our strict security requirements. The ability to manage cipher suites, as well as auto-renewal within our parameters, creates for an available and secure environment."
Head of Information Security — OneTrust
Top Advanced Certificate Manager use cases
Advanced Certificate Manager automates TLS certificate management, even for hundreds of domains and subdomains.
Use the most up-to-date cipher suites for encryption and authentication, and block connections using less secure cipher suites. See our recommendations for the most recent and secure cipher suites.
The default validity period for certificates is 90 days; use shorter ones to reduce the damage from compromise.
Whitepaper
Article
Explore
Explore




Ask about this product
Include the product name and your questions in your enquiry.